Introduction
Government service provider attacks get acute threats due to the large volumes of personal, financial, and identity information stored by them. The extent of the damages in this case can be established by the Service NSW breach during 2020 which caused so much damage when combined with inadequate mailbox controls. In this report, the Cyber Kill Chain framework will be used to analyze the incident and map every phase of the attacks to the most likely MITRE ATT&CK techniques. The analysis can be insightful to the topmost leadership on how the attackers went about ensuring that Service NSW was the targeted enterprise and what could be handy to lead in as far as future resilience may be concerned. Students seeking guidance with cybersecurity concepts and academic report structure can explore best assignment help Australia for additional academic support.
Event Overview
In March 2020, a phishing attack also affected Service NSW in which 47 mailboxes of employees were compromised. IMAP synchronisation gave the attackers an opportunity to take 730 GB of information (3.8 million documents) away. Having tender information, driver licences, passport, birth certificates, financial information, tax file number were sensitive data too. There were approximately 186,000 customers that have been affected (Fadzil et al., 2023). There were urgent steps communities had to take and that included credentials reset, multi-factor authentication (MFA), turning off older protocols, and upgrading to Microsoft 365 E5. There was no proved third-party breach although, consequentially, there were financial, reputational and governance impacts, with cost to litigate the breach is above A$30 million.
Kill Chain Analysis
Reconnaissance
- MITRE Tactic: Reconnaissance (TA0043)
- Techniques: Phishing information (T1598), collecting employee information in the social media (T1589)
The targeting criteria were evident: Service NSW represented a centralised hub of the services, with a valuosity of personal data being involved in the handling of multiple agencies (Muller, 2025), presenting an appealing identity theft target.
Weaponisation & Delivery
The attackers designed phishing emails with virulent links or attachments to get the credentials.
- Tactic: Initial Access (TA0001)
- Techniques: Phishing (T1566.001 -- spearphishing through email)
This was enhanced by legacy authentication configurations that were providing weak security contexts like IMAP logins.
Exploitation & Installation
After gathering credentials, attackers used their vulnerability on the security of mailboxes. They created permanent access by synchronising the IMAP mailboxes.
- Strategies: Persistence (TA0003) and Credential Access (TA0006)
- Techniques: Valid accounts (T1078), use of legacy protocols (T1071.004 - application layer protocols)
This was bypassed by MFA until a stricter control was imposed.
Command & Control
Further despite the lack of reports of any custom malware (Presekal et al., 2024), the very presence of mailbox synchronisation served as a command and control channel.
- Tactic: Command and Control (TA0011)
- Procedure: Application Layer Protocol: IMAP (T1071.004)
Actions on Objectives (Exfiltration)
Data belonging to the attackers was downloaded systematically in weeks and ultimately 730 GB was exfiltrated.
- Tactic: Exfiltration (TA0010)
- Techniques: Exfiltration by application layer over protocols (T1048.003), email collection (T1114.002 - remote email collection)
The failure of the intrusion was not caused by viruses (Malimban et al., 2021), but by the power of exfiltration by legitimate accounts.
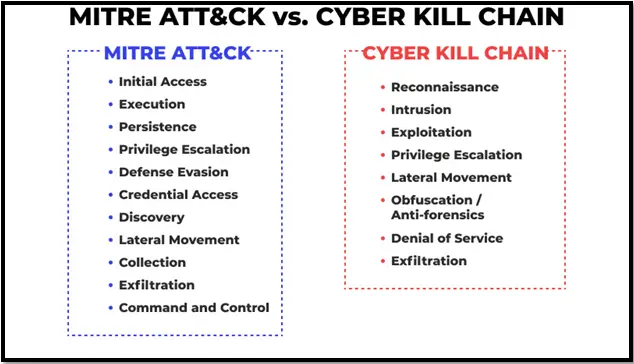
(source: https://www.wallarm.com/what/what-is-the-mitre-attck-framewor)
Target Selection Criteria
The fact the enemies have selected Service NSW was a strategic one:
- Data richness: Saves valuable identity and financial identities (driving licences, TFNs etc.).
- Centred contact point of role: Becomes a frontier between the various agencies, which increases the possible payoff.
- Weaknesses as perceived: Phishing was enhanced by legacy authentication protocols that were not implemented with a stringent and rigid MFA utilization.
- High impact leverage: Monetised or otherwise (Yamin & Katt, 2022), the government targets produce reputational pressure and expensive responses.
Discussion and Lessons
The intrusion underlines the use of simple credential theft by the attacksers against complex zero-days (Arsal et al., 2025). Some of the major lessons to senior leader include:
- This is enforced and the default setting of MFA and deactivation of legacy protocols.
- Conduct Phishing exercises and employee training.
- Apply Advanced detection (threat hunting, mailbox anomaly detection).
- Prepare explicit incident response protocols to help to accelerate the notification and decrease fatigue.
- Ensure the governance and communications are in tandem to secure customer loyalty.
Students looking to strengthen their understanding of phishing attacks, threat analysis, and security frameworks can explore Cyber Security Assignment Help for further academic guidance.
Conclusion
The case of Service NSW breach shows that a simple phishing attack can develop and become one of the most noticeable breaches in the sphere of Australian government. Using the Cyber Kill Chain framework, it can be concluded that the attackers were able to conduct all the stages efficiently: reconnaissance done due to OSINT, delivery done through phishing, exploitation done through the use of credentials, and exfiltration done through mailbox synchronisation. According to the MITRE ATT&CK mapping, the familiar non-new tricks techniques were the cause. The identity information of the attackers was quite important and Service NSW was chosen due to its centrality. The case shows to organisations that there is urgent need to take the initiative to defend, to be ready and to invest in secure configurations to enable that there is interaction between the human, technical and governance layers.
Reference List
- Arsal, M., Asad, H., Kamel, T., & Khan, A. (2025, August). Cyber-Safety Assessment of Wind Turbines: A Reachability Analysis Approach Against Cyber-Attacks. In International Conference on Computer Safety, Reliability, and Security (pp. 340-354). Cham: Springer Nature Switzerland.
Retrieved From: openaccess.city.ac.uk [Retrieved On: 5.9.25] - Fadzil, L.M., Manickam, S. and Al-Shareeda, M.A., 2023, February. A review of an emerging cyber kill chain threat model. In 2023 Second International Conference on Advanced Computer Applications (ACA) (pp. 157-161). IEEE.
Retrieved From: researchgate.net [Retrieved On: 5.9.25] - Malimban, J., Payne, B. R., & Abegaz, T. T. (2021). Drone hacking: Applying the cyber kill chain to hijack unmanned aerial systems. QRBD, 8, 213.
Retrieved From: faculty.utrgv.edu [Retrieved On: 5.9.25] - Muller, L.P., 2025. Cybersecurity in practice: The vigilant logic of kill chains and threat construction. European Journal of International Security, 10(2), pp.231-251.
Retrieved From: cambridge.org [Retrieved On: 5.9.25] - Presekal, A., Ştefanov, A., Rajkumar, V. S., Semertzis, I., & Palensky, P. (2024). Advanced persistent threat kill chain for cyber-physical power systems. IEEE Access.
Retrieved From: ieeexplore.ieee.org [Retrieved On: 5.9.25] - Yamin, M. M., & Katt, B. (2022). Use of cyber attack and defense agents in cyber ranges: A case study. Computers & Security, 122, 102892.
Retrieved From: ntnuopen.ntnu.no [Retrieved On: 5.9.25]